Penetration testing (pentest): everything you need to know to secure your business in 2026
Manage your IT assets remotely
Discover our all-in-one solution

What if you could discover your security flaws before cybercriminals do? That is exactly the role of a penetration test, also known as a pentest. The concept: simulate real-world attacks on your information system to identify vulnerabilities, measure their impact, and fix them before they can be exploited.
This is not just a theoretical issue. According to the 2026 CESIN barometer on cybersecurity in French companies, 40% of companies experienced at least one significant cyberattack over the past year. And after phishing, exploiting security vulnerabilities remains one of the most common attack vectors.
Definition, types of pentests, methodology, tools, budget: we explain everything you need to know about penetration testing, clearly and without unnecessary jargon.
What is a penetration test?
Defining the pentest
A penetration test (or penetration test, abbreviated as pentest) is a security assessment where experts put themselves in the shoes of an attacker. Their mission: to attempt to penetrate a computer system, a network, a web application, or a cloudenvironment, with the company's written consent and within a scope defined in advance.
In practical terms, the pentester uses the same techniques and the same tools as cybercriminals. They look for security vulnerabilities, attempt to exploit them, and then measure how far they can go: accessing sensitive data, taking control of a workstation, escalating privileges on the internal network, and more.
The goal is not to "break" your information system, but to answer a simple question: what could an attacker actually do in your environment today?
Scenario: a pentester discovers that an old test server, forgotten for two years, is still accessible from the internet. They find plaintext credentials on it, which grant them access to the company's email system. A vulnerability invisible in day-to-day operations, yet critical.
Difference between security audit and penetration testing
The two terms are often confused, yet they address different needs.
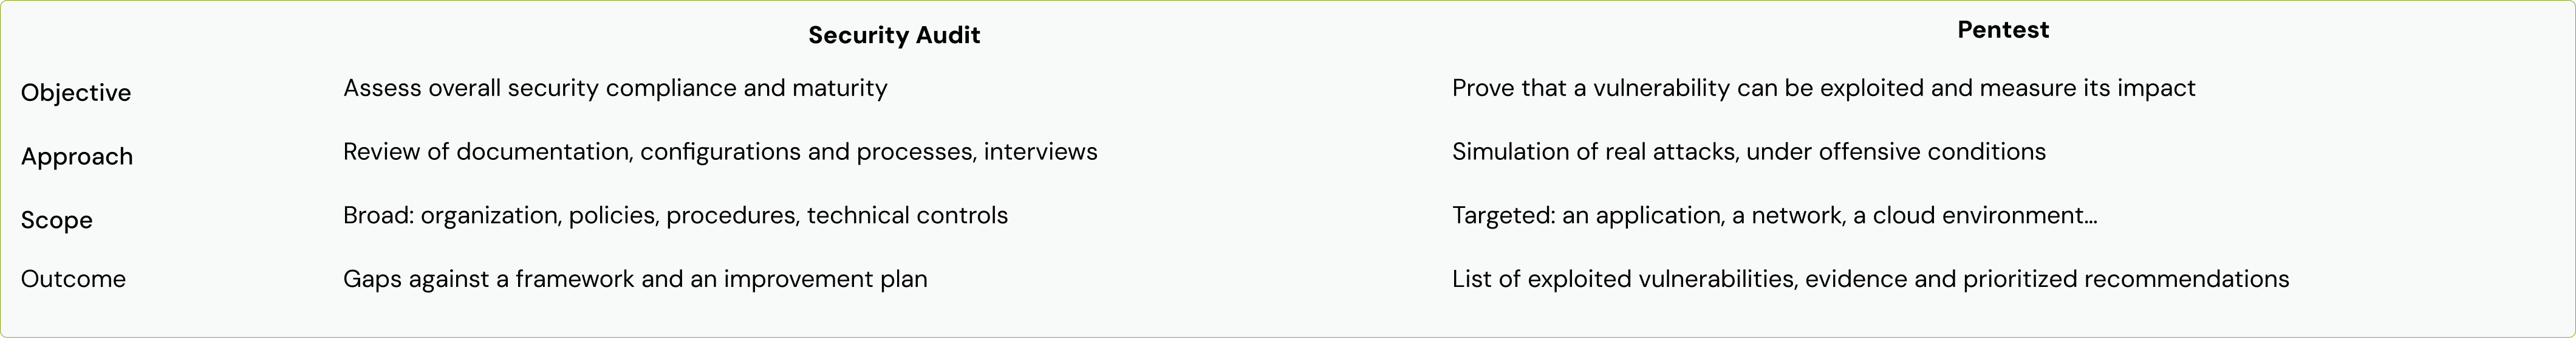
In short, asecurity audit verifies that the right policies are in place, while a pentest verifies that they can withstand an attack. The two are complementary: in fact, penetration testing is often one component of a broader audit.
Why conduct a penetration test for your company?
Firewalls, antivirus software, and updates are essential. But how do you know if everything really holds up against an attack? A penetration test provides a concrete, quantified, and documented answer.
Identify vulnerabilities before cybercriminals do
New vulnerabilities are published every day. A misconfigured cloud, a default password, outdated software, or overly broad access rights are enough to create a breach.
A pentest allows you to detect these potential flaws before they are exploited. And most importantly, it prioritizes them: not all vulnerabilities are equal. A critical flaw exposed on the internet takes precedence over a minor defect accessible only from the internal network.
💡 An automated scanner will flag hundreds of alerts. A pentester, however, tells you which ones are actually exploitable and what they could allow an attacker to access.
Reduce the risk of cyberattacks
Phishing, ransomware, exploit attempts, attacks via a third-party provider... The most common cyberattacks almost always rely on a known but unpatched vulnerability.
By simulating these attacks, penetration testing allows you to:
- reduce the attack surface by closing unnecessary entry points;
- evaluate detection capabilities of your teams and tools (did your SOC spot the intrusion?);
- prioritize cybersecurity investments based on the most significant risks;
- raise awareness among management with concrete evidence rather than abstract scenarios.
This last point is often decisive: a report showing that an attacker was able to access payroll records in two hours carries much more weight than a generic alert.
Complying with regulatory requirements and security standards
Penetration testing is also a driver for compliance. Many cybersecurity standards and regulations require regular testing of the effectiveness of security measures:
- GDPR : Article 32 mandates a process for regularly testing, assessing, and evaluating the effectiveness of technical and organizational measures;
- NIS2 : the European directive requires affected entities to assess the effectiveness of their cyber risk management measures;
- ISO 27001 : the standard requires rigorous management of technical vulnerabilities, and penetration testing is one of the most recognized ways to demonstrate this;
- DORA : for financial entities, the regulation mandates resilience testing, and even threat-led penetration testing for the most significant players;
- PCI DSS : for companies that process card payments, at least one annual penetration test is required.
Beyond regulatory requirements, your clients, partners, and cyber insurer are increasingly asking you to prove your security posture. A recent penetration test report is a strong asset in both tender processes and insurance negotiations.
The different types of penetration tests
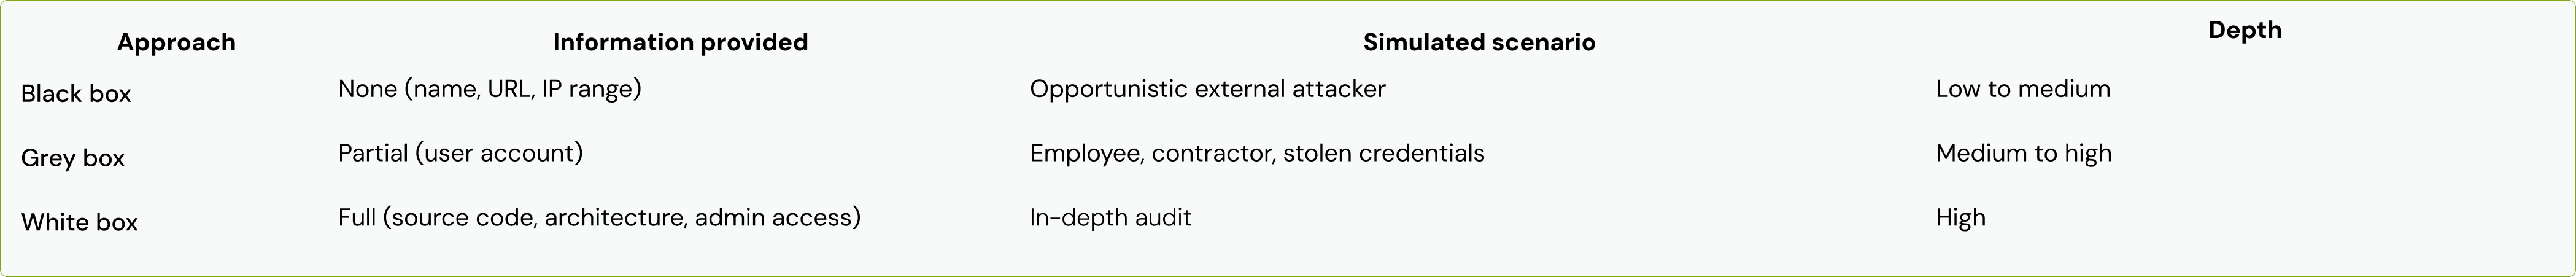
Not all penetration tests are the same. They are primarily distinguished by the level of information provided to the penetration tester (black, grey, or white box), and then by the starting point of the attack (external or internal).
Black box testing
In black boxtesting, the penetration tester has no prior information, other than the company name or a target address. They are in the exact position of an external attacker discovering your organization.
- Advantage: this is the most realistic scenario for facing an opportunistic cybercriminal.
- Limitation: a large portion of the time is spent on reconnaissance, and some areas of the system may remain unexplored.
White box testing
In white boxtesting, it’s the opposite: the pentester has access to everything. Source code, architectural diagrams, documentation, administrator accounts, and more.
- Advantage: it is the most comprehensive approach. It allows for the detection of deep-seated vulnerabilities, particularly within application code.
- Limitation: it requires more time and preparation, and it is less effective at simulating a real-world attack.
Grey box testing
The grey box pentest is a compromise between the two. The pentester has partial information, typically a standard user account. This simulates a malicious insider, a contractor, or an attacker who has stolen credentials via phishing.
This is the most common approach in a corporate setting, as it offers the best balance between realism, depth of analysis, and budget.
External vs. internal penetration testing
Second criterion: where does the attack originate?
- External penetration testing targets everything exposed on the Internet: websites, SaaS applications, email, VPNs, remotely accessible servers, and cloud services. It answers the question: can an attacker get into our systems from the outside?
- Internal penetration testing starts from inside the network, as if the attacker already has a foothold (a compromised workstation, a network jack in a meeting room, or a malicious employee). It answers a different question: Once inside, how far can they go? This is often where the most critical vulnerabilities are discovered, such as a misconfigured Active Directory.
The two are complementary. A network penetration test generally combines an external phase and an internal phase.
How does a penetration test work?
A pentest follows a methodology that is structured and based on recognized frameworks such as the OWASP testing guide (for web applications), the PTES, or the OSSTMM. Before any action is taken, a scoping phase defines the perimeter, objectives, dates, and rules of engagement. Written authorization is essential: without it, a penetration test is legally just an intrusion.
The test then generally proceeds in four main stages.
Reconnaissance and information gathering phase
This is the observation phase. The pentester collects as muchinformation as possible about the target : domain names, subdomains, IP addresses, technologies used, exposed services, employee email addresses, public data leaks, and more.
This collection is done in two stages: passive (using public sources, social networks, and search engines, without direct contact with your systems) and then active (network mapping, open port scanning). The more thorough the reconnaissance, the more realistic the simulated attack will be.
Vulnerability analysis and flaw identification
Based on this mapping, the pentester searches for vulnerabilities : outdated software versions, misconfigurations, weak passwords, exposed unnecessary services, and application flaws (SQL injections, XSS, broken access control, etc.).
They combine automated scanners and manual analysis. Tools quickly find known flaws, but only the human eye can spot business logic flaws—the kind no scanner can detect.
Exploiting security flaws
This is the step that distinguishes a pentest from a simple scan. The pentester attempts toexploit the identified flaws to prove they are real and measure their impact: data access, server takeover, privilege escalation, lateral movement within the internal network, and more.
This exploitation is always controlled : it stops at the demonstration phase and respects the limits set during the scoping process. The goal is to collect evidence, not to disrupt your operations.
Detailed report and recommendations
The final deliverable is the penetration test report. It generally contains:
- an executive summary, readable by management, which summarizes the overall risk level;
- technical details for each vulnerability, including its criticality level, proof of exploitation, and the attack scenario;
- remediation recommendations that are prioritized, concrete, and tailored to your context.
The report is often presented during a debriefing meeting. A best practice is to then schedule a re-test (or follow-up audit) a few weeks later to verify that the corrections have been properly implemented.
Tools and techniques used during a pentest
Pentesters rely on a wide toolkit, often open source, which partially overlaps with the tools needed for daily cybersecurity operations. But tools aren't everything: it is human expertise that turns an alert into a credible attack scenario.
Network analysis and scanning tools
To map a network and identify weak points, a few tools are essential:
- Nmap to discover active machines, open ports, and exposed services;
- Wireshark to analyze network traffic and identify unencrypted communications;
- Nessus or OpenVAS to automatically scan for known vulnerabilities;
- Metasploit to test exploitability of flaws in a controlled manner;
- BloodHound to map attack paths within an Active Directory environment.
Social engineering techniques
The most exploited vulnerability is often human. This is why some pentests include a component ofsocial engineering :
- simulated phishing campaigns to measure click-through and credential entry rates;
- phone calls (vishing) from fake IT support;
- physical intrusion tests, such as attempting to access premises or dropping a compromised USB drive.
👉 Scenario: a "support technician" calls an employee for an urgent update and asks for their MFA validation code. If the employee provides it, all technical security is bypassed in a minute.
These tests are not intended to trap teams, but to identify needs for awareness training and to reinforce good habits.
Web and cloud application testing
Websites, extranets, APIs, SaaS applications: applications are a prime target. Penetration testers use tools like Burp Suite or OWASP ZAP to intercept and manipulate requests, and rely on the OWASP Top 10, the industry standard for the most critical application risks (broken access control, injections, misconfigurations, etc.).
On the cloud side (Microsoft 365, Azure, AWS, Google Cloud), the test focuses on identity and access management, publicly exposed storage buckets, exposed API keys, and default configurations. Tools like ScoutSuite or Prowler help audit these environments. With the widespread adoption of remote work and SaaS, this is often where the most significant risks lie.
Best practices for a successful penetration test
A well-prepared pentest means a better-utilized budget and actionable results. Here are the points you shouldn't overlook.
Clearly define the scope and objectives
Before launching anything, ask yourself the right questions:
- What to test? Website, internal network, Microsoft 365, business applications, workstations, etc.
- Why? Preparing for certification, reassuring a client, validating a new infrastructure, or meeting regulatory requirements.
- Which approach? Black box, grey box, or white box; external or internal.
- What are the limitations? Excluded systems, authorized hours, and prohibited techniques (such as denial-of-service attacks).
A scope that is too broad dilutes the budget, while a scope that is too narrow leaves blind spots. The best approach: start with the most critical and exposed assets.
💡 A well-inventoried IT environment makes scoping much easier. It is difficult to define a scope if you don't know exactly which workstations, accounts, and applications are being used in the company.
Choosing the right cybersecurity provider
Penetration testing is built on trust: you are giving a third party the means to attack your information system. Here are a few criteria to help you choose:
- PASSI qualification (Information Systems Security Audit Provider), issued by ANSSI, which serves as a guarantee of competence and methodology;
- pentester certifications (OSCP, OSWE, CEH…) ;
- a sample report anonymized, to assess the clarity and quality of the recommendations;
- the methodology proposed and the audit agreement, which provides the legal framework for the engagement;
- post-test support : debriefing, remediation assistance, and retesting.
Schedule regular pentests
A penetration test is a snapshot in time. Your information system, however, is constantly evolving: new employees, new applications, cloud migrations, and new vulnerabilities published every week.
To stay protected, integrate pentesting into a continuous process:
- a penetration test at least once a year on critical assets;
- an additional test after every major change (new application, network overhaul, migration);
- between two pentests, a regular vulnerability scan, and updates applied without delay and monitoring of security (SOC, EDR).
Penetration testing does not replace day-to-day security: it verifies it.
Frequently asked questions about penetration testing
What is the ideal frequency for conducting a pentest?
The most common recommendation is to conduct a penetration test at least once a year, and after any significant change to the information system, such as launching a new application, migrating to the cloud, or changing network infrastructure. Some regulations, like PCI DSS, actually mandate this annual cadence. Highly exposed companies often opt for more frequent testing, or even continuous pentesting.
How much does a penetration test cost?
The price mainly depends on the scope, theapproach (black, grey, or white box), and the number of days required. Pentests are generally billed at a daily rate. As a rough guide, expect to pay a few thousand euros for a limited scope, such as a simple web application tested over a few days, and tens of thousands of euros for a comprehensive test combining internal and external networks, cloud, and social engineering. Always request a detailed quote following a scoping phase.
Can a pentest damage my IT system?
The risk exists, but it is very low when the test is properly managed. Professional pentesters work under strict rules of engagement, avoid destructive techniques, and stop once they have proof of exploitation. To be even more cautious, you can exclude the most sensitive systems, set specific time slots, perform certain tests in a pre-production environment, and ensure that your backups are up to date before starting.
Who can perform a penetration test in my company?
A penetration test should be entrusted to offensive security experts, whether internal or external, with written authorization from management. In most SMEs, it is carried out by a specialized service provider, ideally one with PASSI qualification from ANSSI. Hiring an independent third party offers another advantage: an outside perspective, free from blind spots or biases regarding your own infrastructure.
In summary: penetration testing is the best way to know where you stand
Penetration testing is not just for large corporations. By simulating real-world attacks, it shows you exactly where your vulnerabilities lie, what an attacker could do with them, and how to fix them. Whether black, grey, or white box, external or internal: the key is to choose the approach best suited to your risks, clearly define the scope, and repeat the exercise regularly.
But a pentest is only valuable if its recommendations are implemented and then maintained over time. That is where it all comes together.
At rzilient, we help you secure your IT on a daily basis : inventory and fleet management, updates, access management, team awareness training, and monitoring with a managed SOC. With our managed cybersecurity offering, your teams can focus on their core business, while your information system remains managed and secure.